B BROCENT

phishing simulation

Cover image for Brocent IT blog post: Ten Employees Clicked the Fake Invoice: Phishing Simulation at a Singapore Trading Company

September 11, 2026 | 15 min

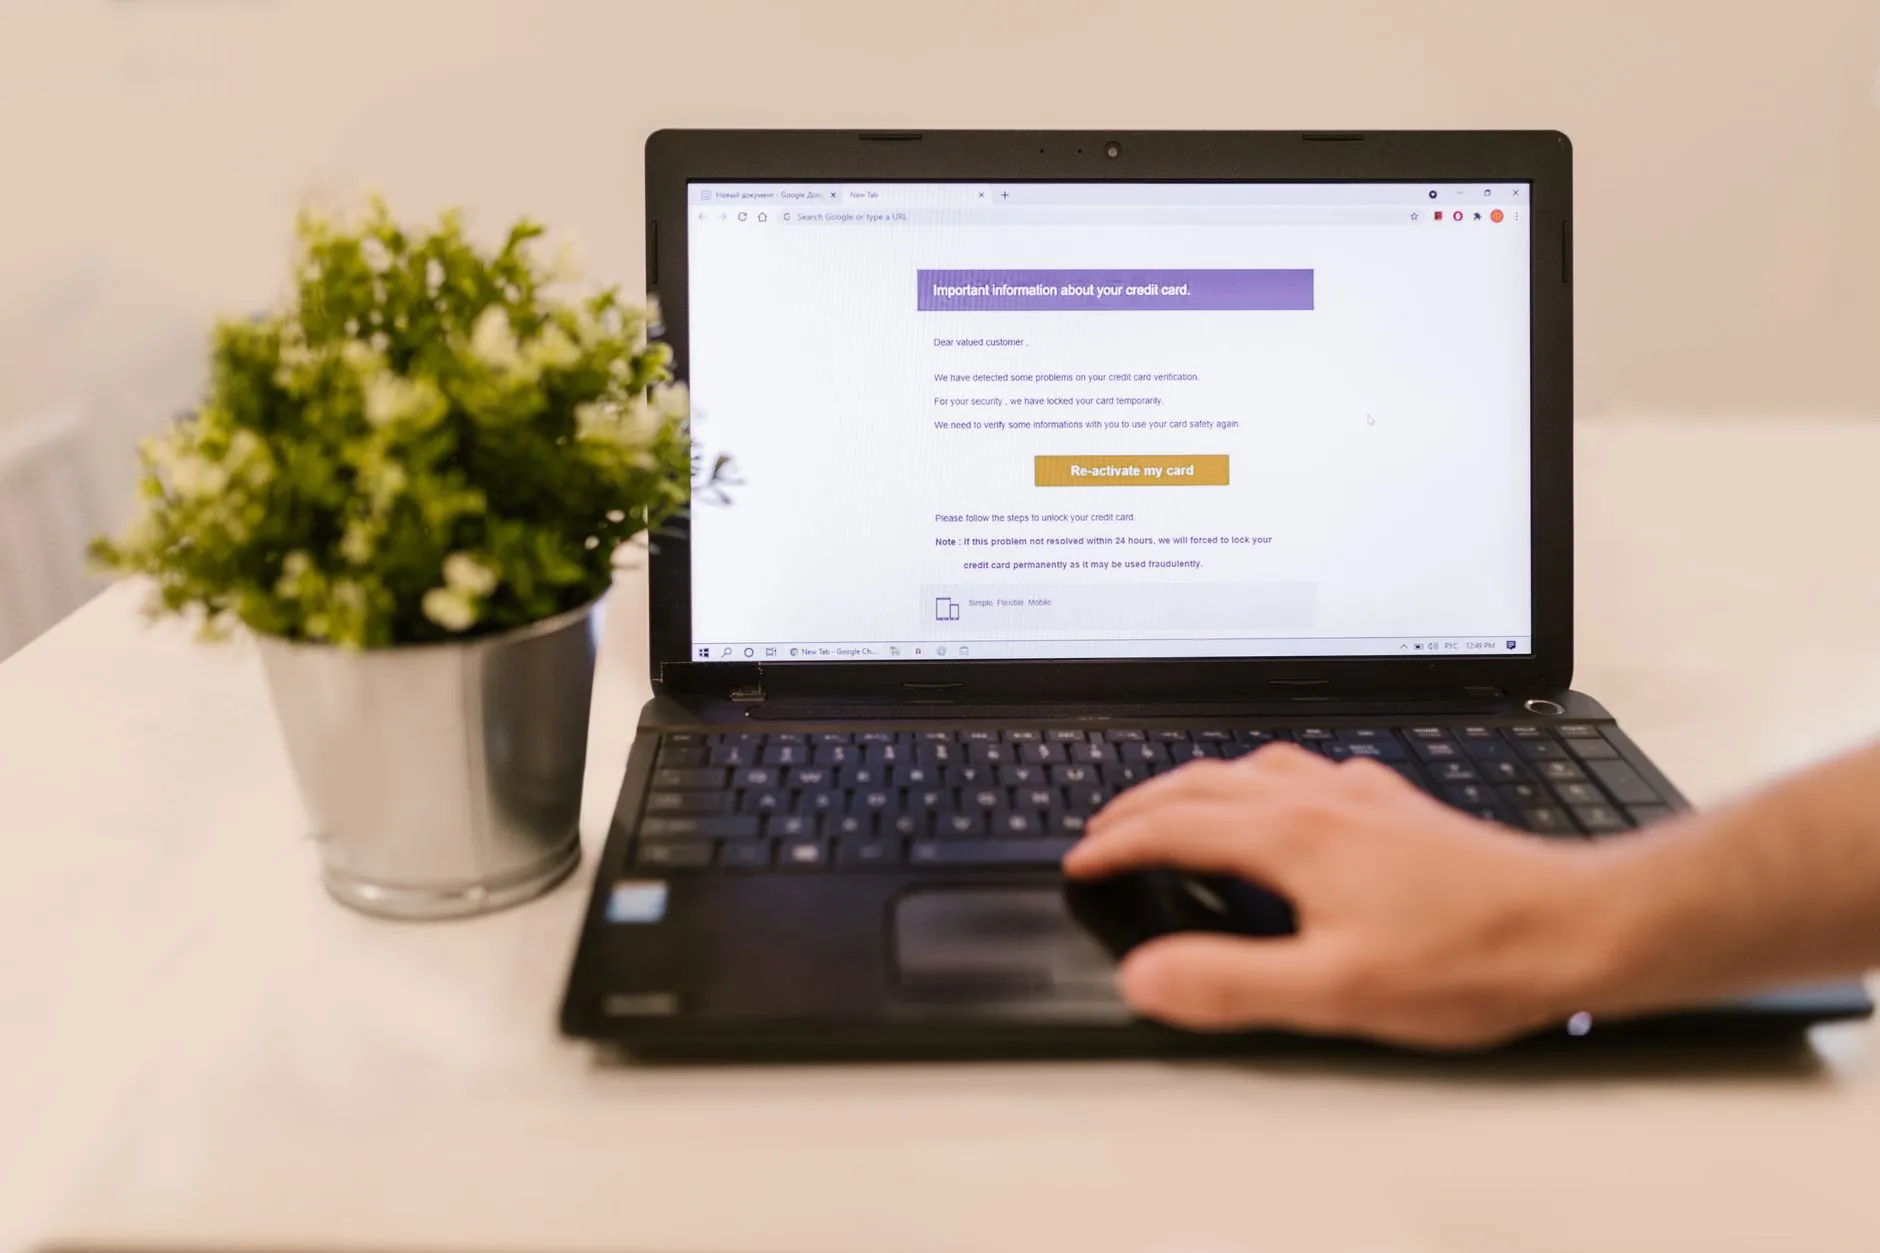
Ten Employees Clicked the Fake Invoice: Phishing Simulation at a Singapore Trading Company

A composite scenario from Singapore: a 70-person trading company runs its first phishing simulation almost as an afterthought, and ten people click a fake supplier invoice in a single afternoon. How to read a first click-rate, why zero reports is a worse signal than ten clicks, and why the programme — not the platform licence — is the thing that changes outcomes.
Cover image for Brocent IT blog post: The Invoice That Almost Went Through

September 04, 2026 | 15 min

The Invoice That Almost Went Through

A composite scenario from Hong Kong: a small marketing agency nearly pays a fraudulent supplier invoice, caught only because a staff member happens to phone to confirm. Why the one cybersecurity video every new hire watches once isn't training, and what a managed, measured awareness programme changes instead.
Cover image for Brocent IT blog post: KnowBe4 Alternative for APAC Teams: What to Look for in a Security Awareness Program

July 14, 2026 | 9 min

KnowBe4 Alternative for APAC Teams: What to Look for in a Security Awareness Program

Comparing KnowBe4 against APAC-native security awareness training options — contract terms, localization, support timezones, pricing, and bundling with a broader security baseline.

Cover image for Brocent IT blog post: Why Phishing Simulation Programs Fail in Asia (And How to Fix Them)

July 14, 2026 | 14 min

Why Phishing Simulation Programs Fail in Asia (And How to Fix Them)

Most phishing simulation programs sold in Asia are US/EU templates with the language swapped out. Here's why they underperform — and what a properly localized, quarterly-cadence program looks like.