cybersecurity
November 12, 2026 | 9 min
Law Firm IT Security Checklist for Hong Kong: PDPO, Document Systems and Cyber Insurance Evidence
Ten IT security checks for Hong Kong law firms, with the evidence to keep for each: identity, email fraud, document access, devices, backups, scanning, logs, provider contracts and cyber insurance.
November 06, 2026 | 10 min
IT Security Audit in Hong Kong: Scope, Cost and What You Get (2026)
What an IT security audit in Hong Kong covers, how it differs from a vulnerability scan, penetration test and IT assessment, the cost drivers, sample deliverables, how to prepare, and which audit fits an insurer, client or privacy review.
October 23, 2026 | 15 min
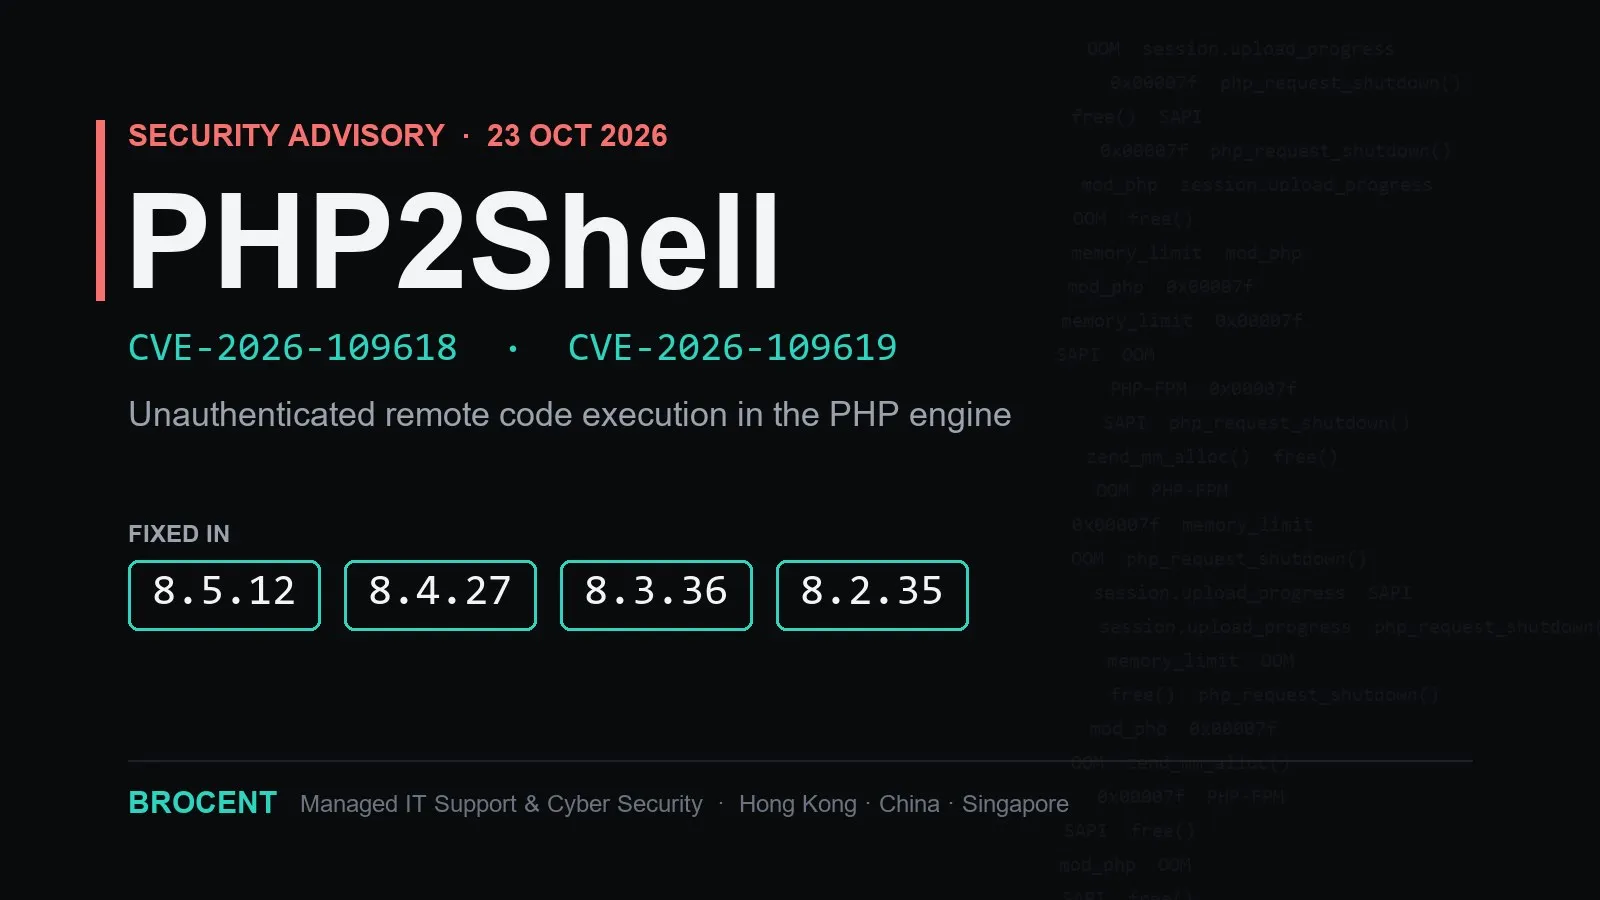
PHP2Shell (CVE-2026-109618 & CVE-2026-109619): Security Report and Response Plan
A security report on PHP2Shell, the two critical PHP engine flaws fixed on 21 October 2026: what they are, who is most at risk, which versions are fixed, what HKCERT, Singapore's CSA and CISA advise, and a 24-hour, 72-hour and 7-day response plan for businesses in Hong Kong, China and Singapore.
October 08, 2026 | 16 min
What Is a Security Operations Center (SOC)? Services, Staffing and Cost (2026)
What a security operations center (SOC) is and does, what security operations center services include, why 24/7 coverage needs about five analysts per seat, how SOC services are priced in Hong Kong and Asia, how to choose a provider and what the monthly report should show.
September 25, 2026 | 20 min
The Report Has to Satisfy Their Bank: Penetration Testing for a Hong Kong Fintech Under Counterparty Review
For the founder or head of engineering at a 15-40 person Hong Kong fintech whose banking counterparty has made a penetration test report a condition of onboarding. Who actually reads the report and what they need to write down, the four things that make a report acceptable, how to scope the test to the relationship, why the cheapest scan fails and the biggest engagement overshoots, planning backwards from the deadline, the re-test small teams forget to negotiate, handling findings you cannot fix in time, and reusing the report for the next counterparty.
September 16, 2026 | 23 min
The Rising Cost of Cybersecurity Incidents: What It Means for IT Service Providers and the Companies That Hire Them
A research report on the economics of cybersecurity incident cost: why the headline breach-cost figure and the average insurance claim differ by two orders of magnitude and both are correct, what Hong Kong and Singapore's own published data does and does not contain, why cyber premiums are falling while breach costs rise, and how to budget security into an IT decision without quoting the wrong population's number.
September 11, 2026 | 15 min
Too Small for Enterprise Security, Too Exposed to Skip It: A Hong Kong Design Studio's Starter Bundle
A composite scenario from Hong Kong: a fifteen-person design studio receives three security quotes, all scoped for a company several times its size, and concludes that real security is out of reach. What a fixed-price starter bundle changes about that decision — and why it is the first rung on the same ladder as a full managed IT plan.
September 11, 2026 | 15 min
Ten Employees Clicked the Fake Invoice: Phishing Simulation at a Singapore Trading Company
A composite scenario from Singapore: a 70-person trading company runs its first phishing simulation almost as an afterthought, and ten people click a fake supplier invoice in a single afternoon. How to read a first click-rate, why zero reports is a worse signal than ten clicks, and why the programme — not the platform licence — is the thing that changes outcomes.
September 04, 2026 | 14 min
The Board Asked Who Owns Cybersecurity: A Hong Kong Firm's vCISO Answer
A composite scenario from Hong Kong: a professional-services firm's board asks who actually owns cybersecurity, and the honest answer is that it's split across the office manager, the outsourced IT vendor, and nobody in particular. Why a fractional CISO — not a full-time hire, and not leaving it with the IT vendor — closes that gap, and what the engagement actually looks like alongside a managed IT plan.
September 04, 2026 | 9 min
SOC as a Service in Hong Kong: What's Included, Pricing Models & SLAs (2026)
SOC as a service in Hong Kong explained: what a security operations center service includes, the pricing models providers use, the SLA terms to put in the contract, how it differs from NOC monitoring and MDR, and a short case study from a multi-outlet retailer.
September 04, 2026 | 15 min
The Invoice That Almost Went Through
A composite scenario from Hong Kong: a small marketing agency nearly pays a fraudulent supplier invoice, caught only because a staff member happens to phone to confirm. Why the one cybersecurity video every new hire watches once isn't training, and what a managed, measured awareness programme changes instead.
September 04, 2026 | 17 min
Three Weeks to Launch, No Pen Test Booked
A composite scenario from Hong Kong: a tech startup's public launch date is set, and someone finally asks whether the app has been pen-tested three weeks before go-live. What actually fits into the time that's left, and why the test needs to be planned against the launch date, not squeezed in after it.
September 04, 2026 | 14 min
The Patch That Was Three Months Overdue: A Hong Kong Firm's Ransomware Near-Miss
A composite scenario from Hong Kong: a backup catches a ransomware attempt mid-way through, and the post-incident review traces the entry point back to a server patch that had been sitting overdue for three months on a system nobody was tracking. What changes when patching becomes a managed, visible discipline instead of a task someone has to remember.
September 04, 2026 | 15 min
The Password Reuse Nobody Flagged: MFA Rollout at a Hong Kong Accounting Firm
A composite scenario from Hong Kong: a routine IT review at an accounting firm finds a staff member reusing the same password across email and the practice-management system, with no MFA on either. Why the fix isn't a stricter password policy, and what a properly designed MFA and conditional access rollout actually looks like alongside a managed IT plan.
September 04, 2026 | 15 min
The Router From the Telco Wasn't Enough: A Hong Kong Manufacturer's Managed Firewall Upgrade
A composite scenario from Hong Kong: a light-manufacturing SME had run for years on the router its telco bundled in with the internet line, until a routine security review found no real firewall policy at all — just factory defaults on a network that had grown to include production-floor equipment alongside office PCs. Why a managed, SME-scale next-gen firewall — not an enterprise offering, and not the telco's bundled router — closed that gap, and what it looks like bundled into a managed IT plan.
August 28, 2026 | 22 min
Why Hong Kong Companies Are Bundling MSP, MSSP, and HKMA/C-RAF Support Into One Contract
A research report on why Hong Kong companies — especially HKMA-regulated authorized institutions and their vendors — are bundling managed IT (MSP), managed security (MSSP), and HKMA cybersecurity/C-RAF regulatory support into a single RFP, what C-RAF's three components actually require, and where a vendor's honest role ends and the institution's own non-delegable regulatory accountability begins.
August 28, 2026 | 15 min
Why a Singapore Fintech's Cyber-Insurance Renewal Came Down to One Vulnerability Scan
A composite scenario from Singapore's fintech sector: a cyber-insurance broker asks for a current, dated vulnerability-scan report, and nobody in the office has one. What insurers are actually asking for, and what a real recurring scanning practice looks like.
August 18, 2026 | 12 min
How to Run an Incident-Response Tabletop Exercise Using ChatGPT-Generated Scenarios
How to build and run an incident-response tabletop exercise with AI-generated scenarios: the four inputs, timed injects, a worked 120-person ransomware run, and why the debrief is the deliverable.
August 18, 2026 | 12 min
How to Use Grok to Track Emerging Security Threats and Vendor Advisories
A practical daily workflow for AI-assisted threat monitoring: build the watchlist from your own estate, verify every hit against the vendor advisory and CISA KEV, then act.
August 09, 2026 | 12 min
How to Use Claude to Flag Phishing Attempts in Business Email
A practical guide to AI-assisted phishing triage: what to feed the model, how a "report suspicious" mailbox workflow works, and the hard limits that keep it a supplement to real email security.
August 07, 2026 | 15 min
IT Disaster Recovery Hong Kong: A Brokerage's Wake-Up Call
How a Hong Kong insurance brokerage discovers the gap between having backup and having real disaster recovery, and what monitored backup and restore drills actually look like.
July 14, 2026 | 9 min
KnowBe4 Alternative for APAC Teams: What to Look for in a Security Awareness Program
Comparing KnowBe4 against APAC-native security awareness training options — contract terms, localization, support timezones, pricing, and bundling with a broader security baseline.
July 14, 2026 | 15 min
Vulnerability Management vs Penetration Testing (and Patch Management): 2026 Guide
A practical guide for APAC SMEs on the difference between continuous vulnerability management and point-in-time penetration testing, when each is required by SFC, MAS, HKMA, or PCI-DSS, and how to decide which to invest in first.